Secure AI Atlas mark Secure AI Atlas SECURITY & GOVERNANCE

Risk observation system

Secure AI Atlas

A technical map of operational risk in generative AI systems.

The focus is not the model in isolation. It is the point where language connects to data, identity, tools, permissions, and decisions—and where useful capability can acquire operational authority.

Each entry turns that surface into something reviewable: a failure mode, a control boundary, or a governance question supported by evidence.

A reading method for AI systems

AI Operational Risk Stack

For each AI use case, ATLAS maps what the system can do, what it can reach, what constrains it, and who has accepted the remaining risk.

Governance Layer

Who has accepted the remaining risk?

Defines what is allowed, who is accountable, what evidence is required, and which risks remain unacceptable.

Control Layer

What constrains it?

Applies identity, permissions, validation, logging, approval, monitoring, sandboxing, and secure implementation.

Exposure Surface

What can it reach?

Maps data, tools, APIs, repositories, workflows, users, and decisions within reach of the system.

AI Capability

What can it do?

Identifies generation, retrieval, reasoning, transformation, tool invocation, recommendation, and action.

ATLAS reads the stack in both directions: from governance down to implementation, and from capability up to organizational risk.

Observation field

Enterprise copilots, RAG systems, AI Agents, and connected tools—especially when their output can affect data, access, or action.

Method

Start with a concrete failure mode, trace its exposure path, identify the control boundary, and ask what evidence would make the risk reviewable.

Coordinates

ATLAS links risks such as Shadow AI and Prompt Injection to practical controls, accountable owners, and governance decisions.

Featured research briefing

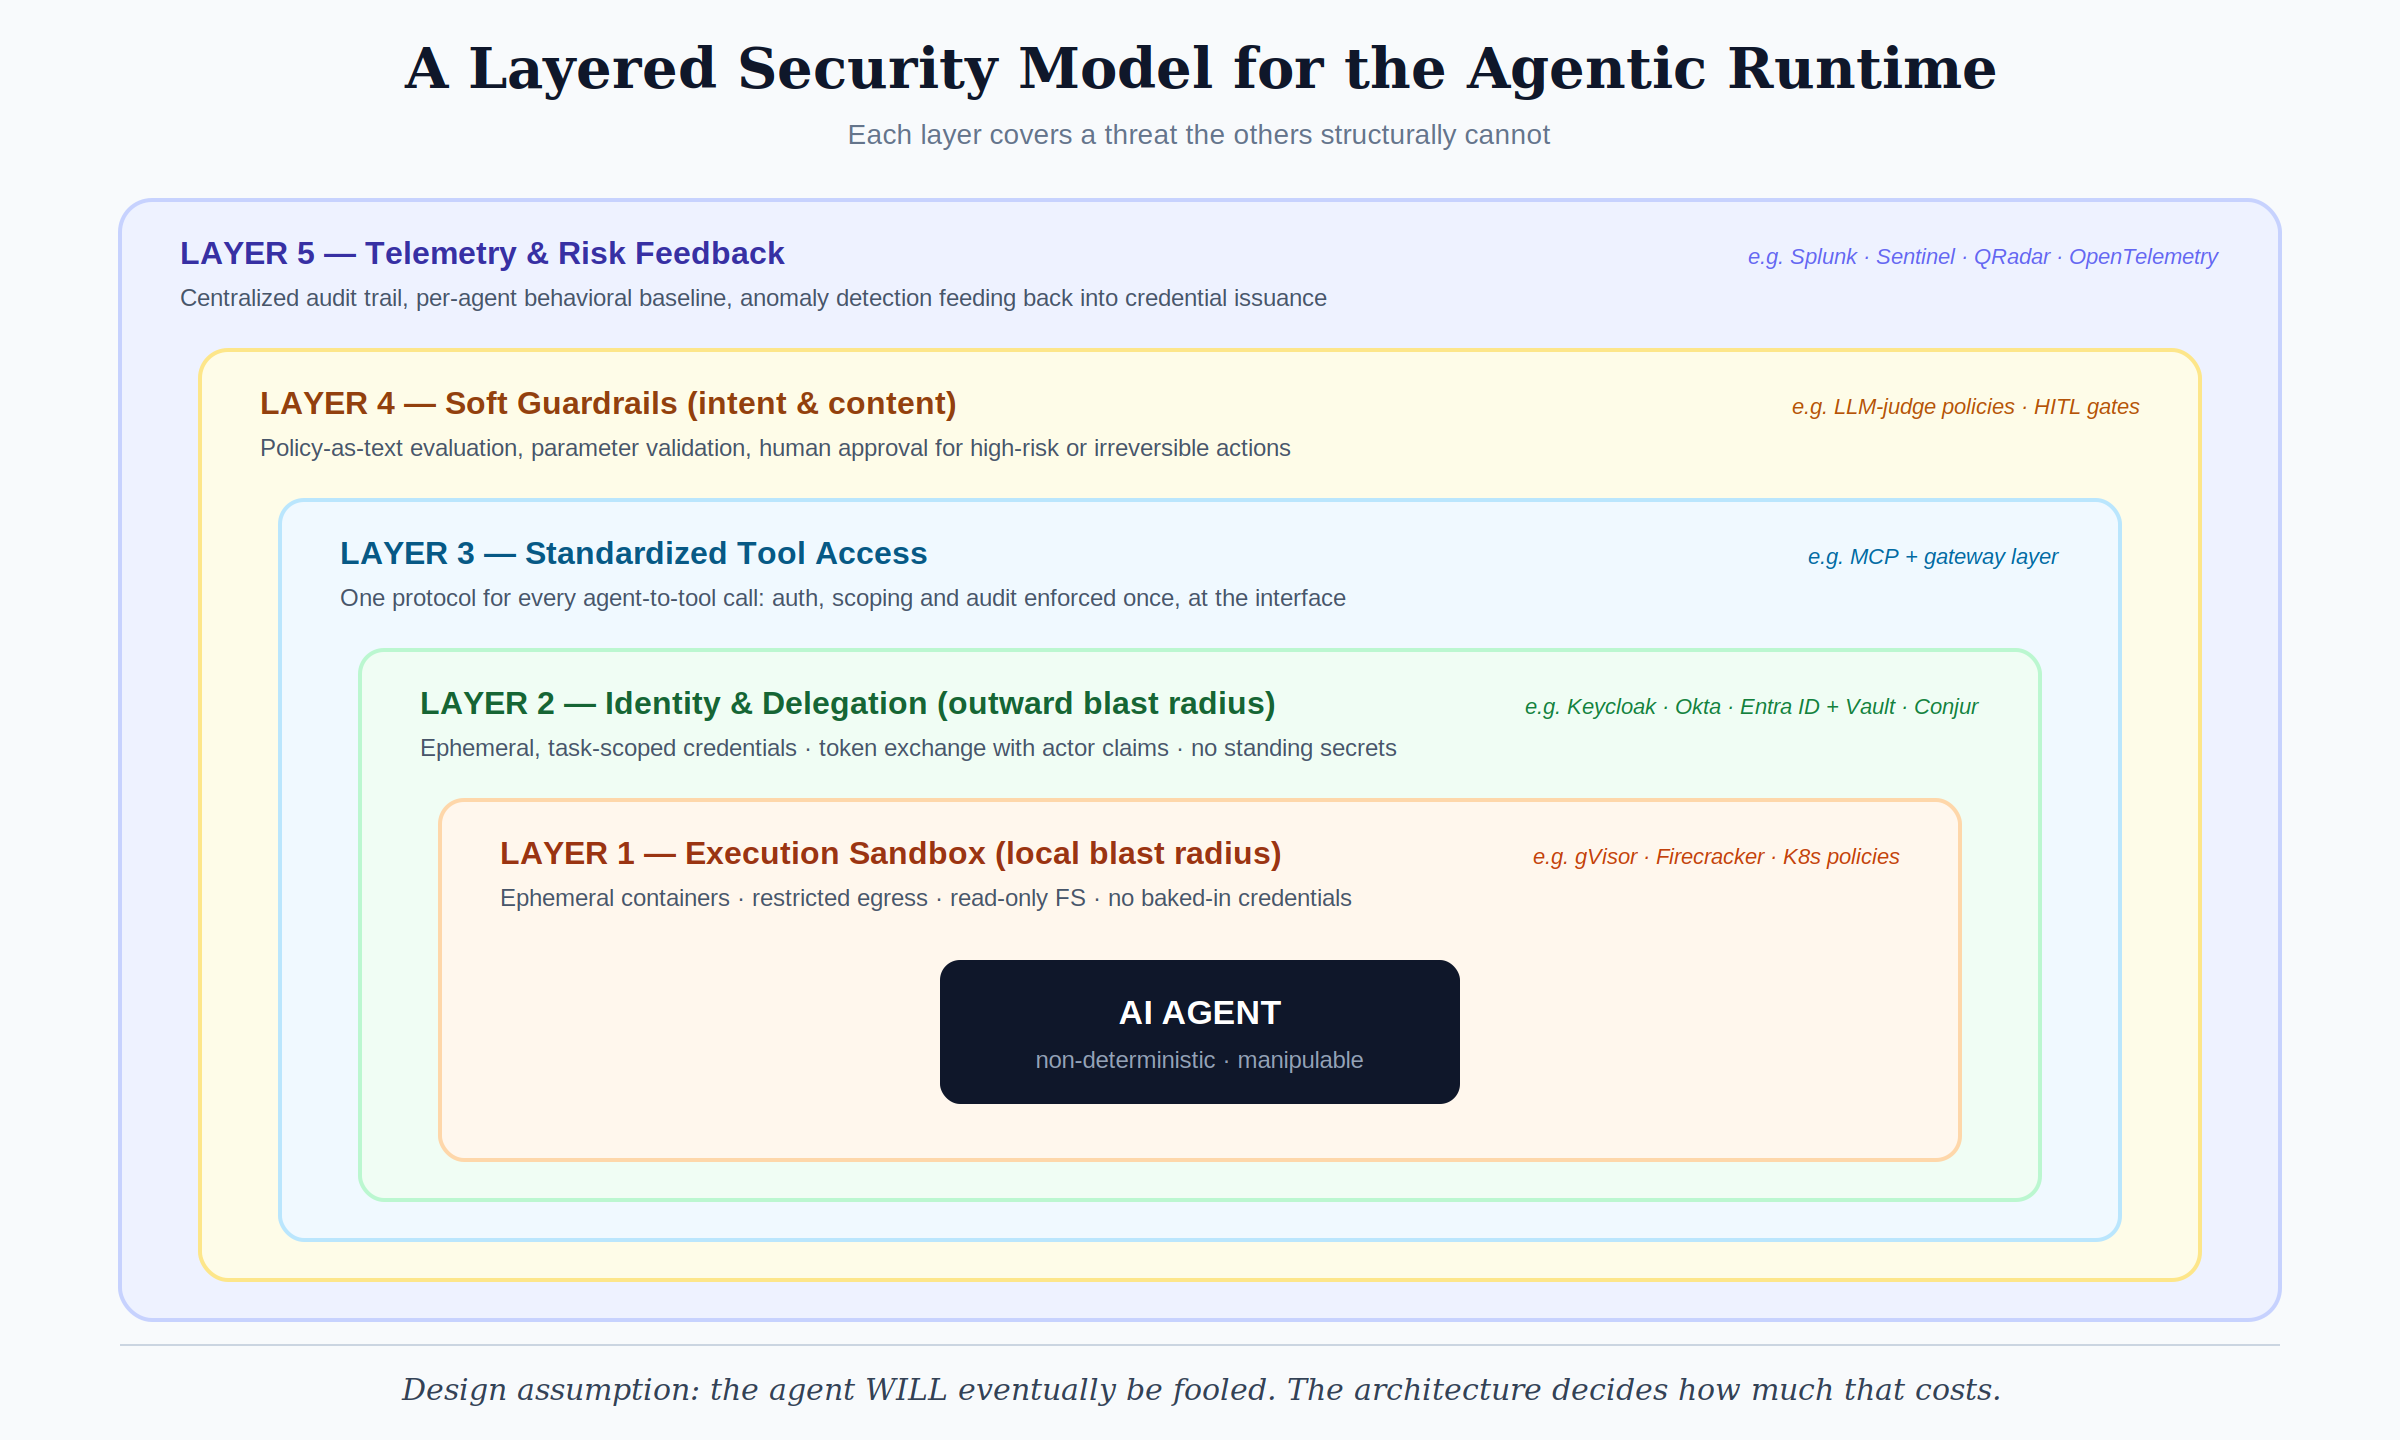
Your AI Agent Has More Permissions Than Your Intern. And No One Gave It a Contract.

Why delegating full identity to AI agents is a time bomb, and a five-layer architecture to defuse it before the first incident.

Recent analysis

Short technical articles for understanding the exposure before selecting a control.

All articles

Risk Catalogue

13 entries

Failure modes that emerge when language crosses into data, identity, tools, permissions, and decision paths.

Data and Model Poisoning

Training data, fine-tuning datasets, or embeddings are deliberately manipulated to introduce vulnerabilities, backdoors, or biases that compromise model security and behaviour.

Improper Output Handling

Model-generated output is passed to downstream systems without validation or sanitisation, enabling injection attacks through AI-generated content.

Misinformation

The model generates false or misleading information presented with apparent authority, which users may accept without verification, with legal, reputational, or security consequences.

Controls Catalogue

7 entries

Operational boundaries that make AI capability observable, constrained, reviewable, and accountable.

Approved AI Tool Register

A maintained record of approved AI tools, allowed use cases, owners, data limits, account requirements, and review status.

Frameworks

7 entries

Industry standards and regulations that define what evidence, controls, and governance structures AI systems require.

OWASP Top 10 for LLM Applications 2026

The definitive industry standard identifying the ten most critical security risks for applications powered by large language models, updated for 2026 with refined rankings, new threat categories, and mappings to MITRE ATLAS, CWE, and NIST AI RMF.

OWASP Top 10 for Agentic AI Applications 2025

A dedicated top-10 list addressing the unique security challenges of agentic AI systems — where LLMs plan, execute multi-step tasks, invoke tools, and operate with delegated authority over enterprise systems.

A technical map, not a risk score

Use the catalogues to frame a review, then use Frameworks to connect findings to owners and evidence. Learning Log records how the map changes as the field develops.

Secure AI Atlas is built to make AI systems legible before capability becomes authority.