Secure AI Atlas mark Secure AI Atlas SECURITY & GOVERNANCE

Risk observation system

Secure AI Atlas

A technical map of operational risk in generative AI systems.

The focus is the point where language connects to data, identity, tools, permissions and decisions—and where useful capability can acquire operational authority.

Each entry turns that surface into something reviewable: a failure mode, a control boundary, or a governance question supported by evidence.

A reading method for AI systems

AI Operational Risk Stack

For each AI use case, ATLAS maps what the system can do, what it can reach, what constrains it, and who has accepted the remaining risk.

Governance Layer

Who has accepted the remaining risk?

Defines what is allowed, who is accountable, what evidence is required, and which risks remain unacceptable.

Control Layer

What constrains it?

Applies identity, permissions, validation, logging, approval, monitoring, sandboxing, and secure implementation.

Exposure Surface

What can it reach?

Maps data, tools, APIs, repositories, workflows, users, and decisions within reach of the system.

AI Capability

What can it do?

Identifies generation, retrieval, reasoning, transformation, tool invocation, recommendation, and action.

ATLAS reads the stack in both directions: from governance down to implementation, and from capability up to organizational risk.

What ATLAS maps

Enterprise copilots, RAG systems, AI agents and connected tools — where output can affect data, access or action.

Start from a concrete failure mode, trace its exposure path, identify the control boundary, and ask what evidence would make the risk reviewable.

The ATLAS model

Risk → Control → Framework → Evidence

Four links, one reviewable chain. Start from the exposure, find the response, check the external reference, then prove the control operates.

Featured research briefing

Your AI Agent Has More Permissions Than Your Intern. And No One Gave It a Contract.

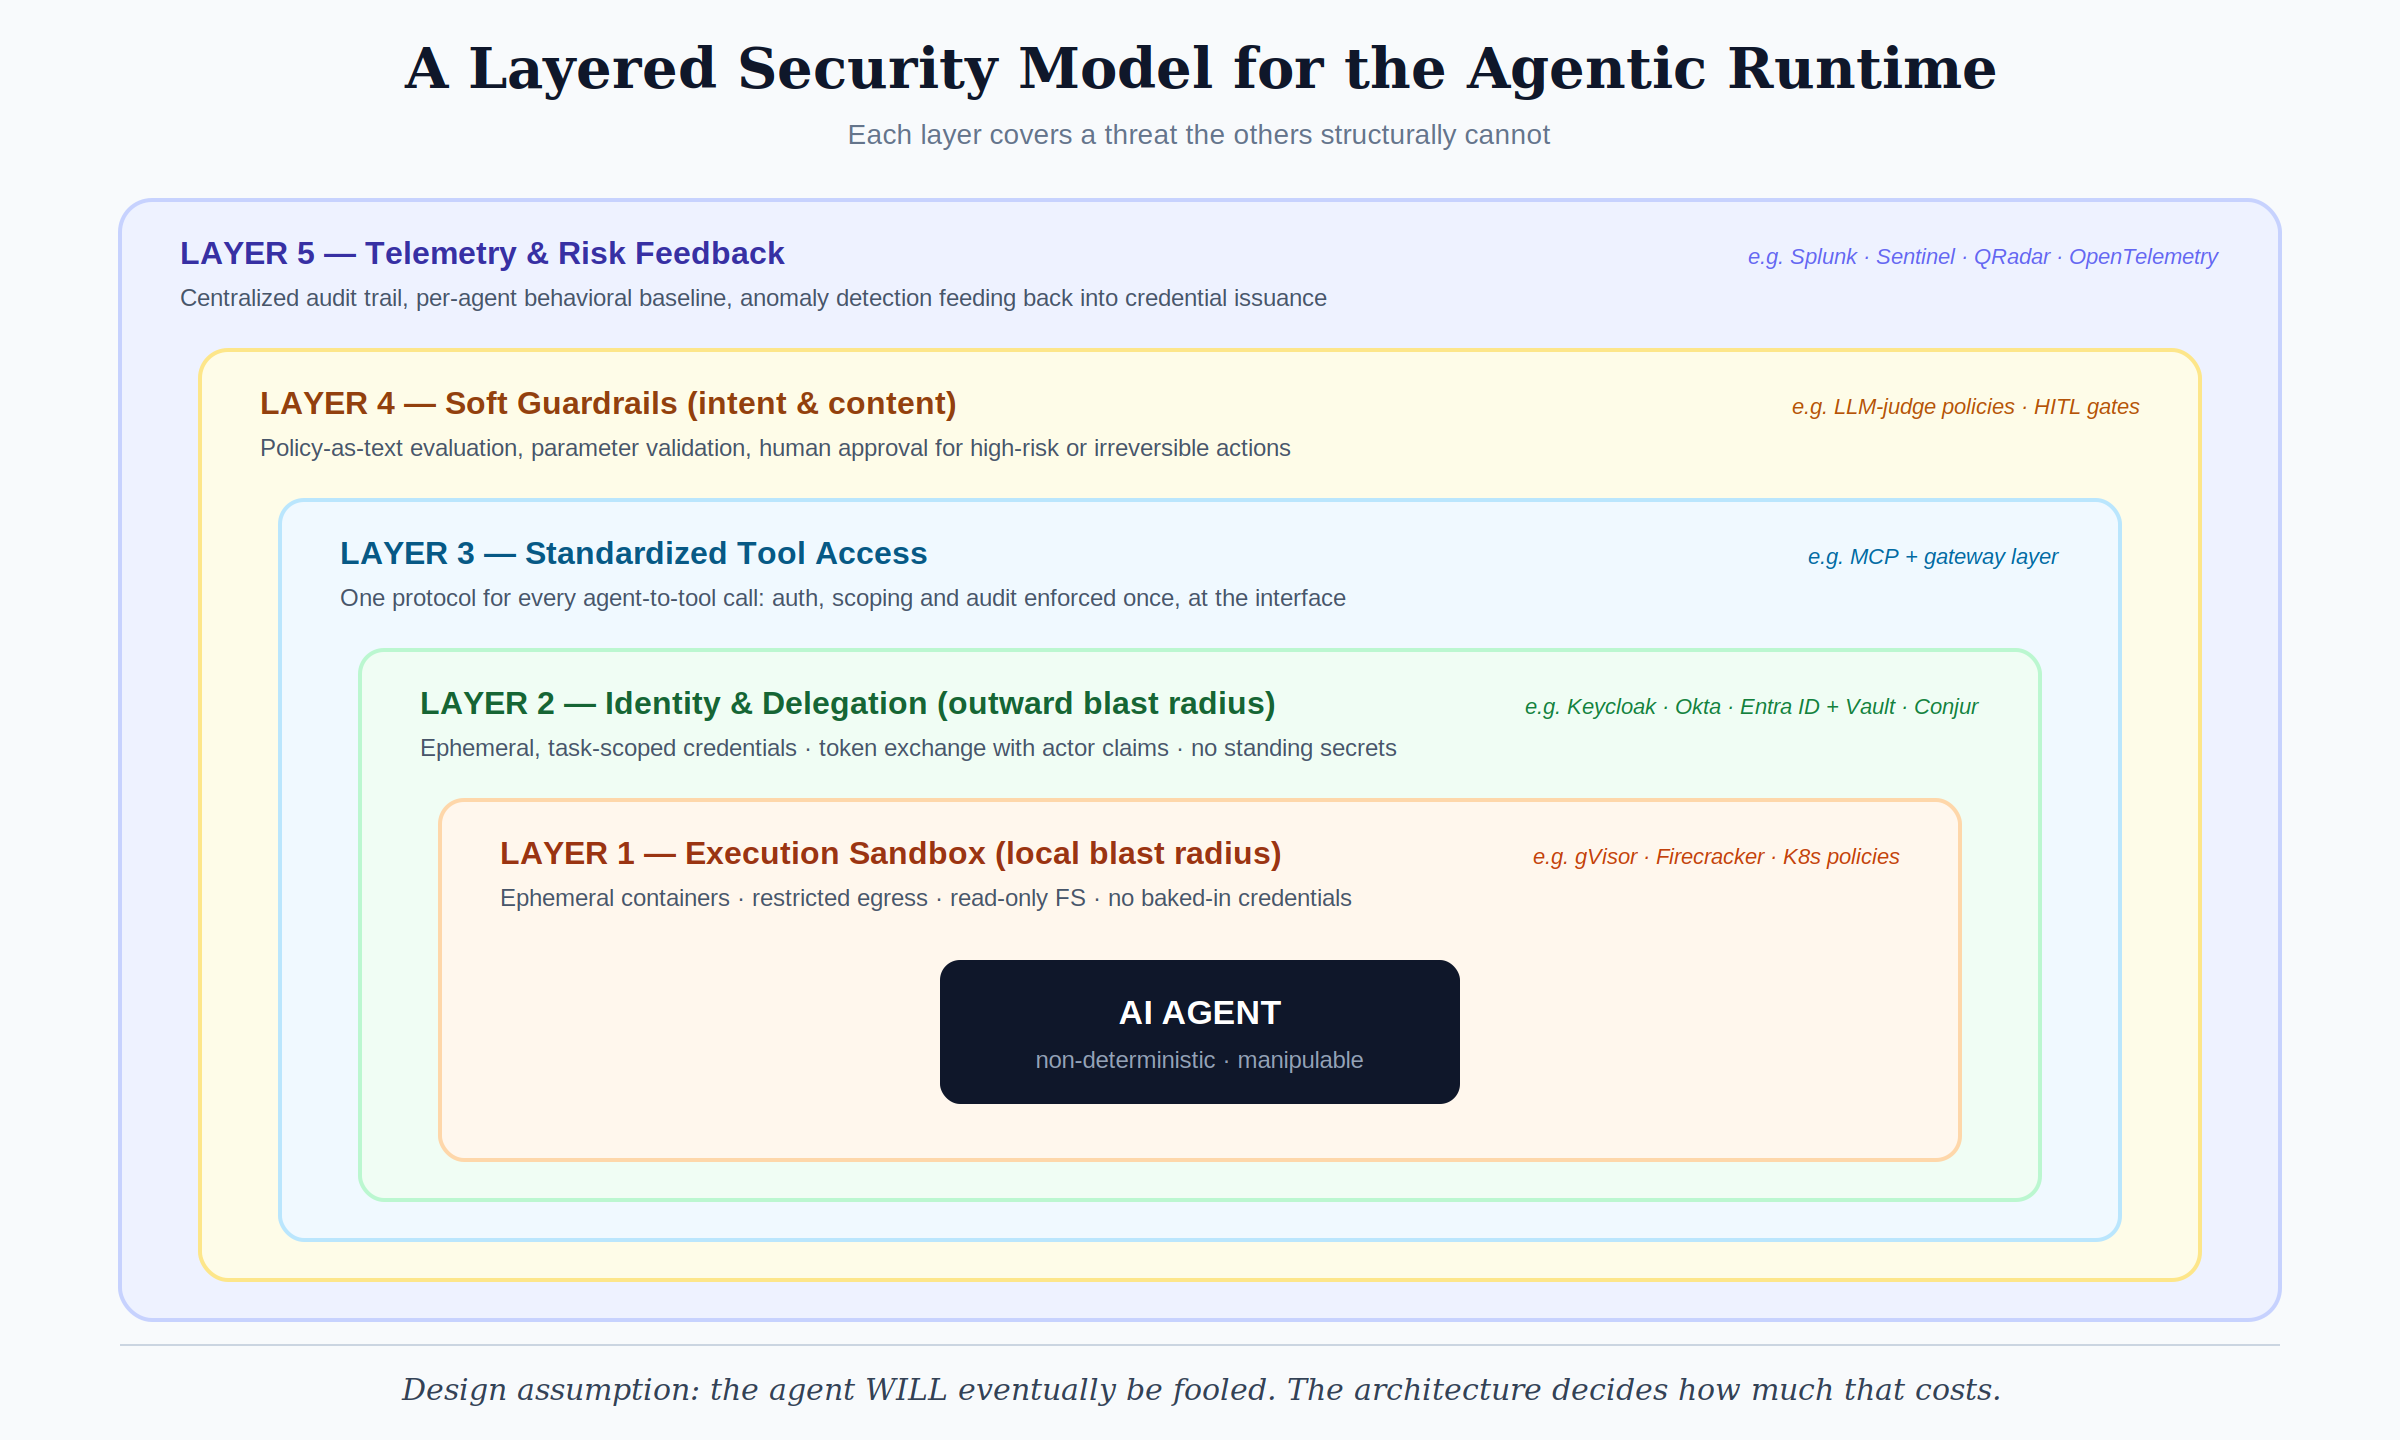
Why delegating full identity to AI agents concentrates unmanaged risk, and a five-layer architecture to constrain it before the first incident.

Recent analysis

Short technical articles for understanding the exposure before selecting a control.

All articles

Another place

Boundary Conditions

A publication kept inside this atlas, with its own register, its own editorial rules and its own reasons to refuse an answer.

Documented incidents, demonstrated mechanisms, argued verdicts, hard scientific questions and conditional scenarios, each graded by the evidence behind it. What it holds is best read where it is printed; this band only marks the way in.

Cross into the register

External intelligence

Atlas Tech Radar

Recent external signals on AI security, agentic systems and governance.

View all signals (56) →

Explore the Map

The four catalogues form one reviewable chain: risk, control, framework and evidence. Open the map to move through them.

A technical map for governed review

Use the catalogues to frame a review, then use Frameworks to connect findings to owners and evidence. Learning Log records how the map changes as the field develops.

Secure AI Atlas is built to make AI systems legible before capability becomes authority.